Fewer employees opened the fake link after information or practice
At a Dutch ministry, about one-third visited the test link without intervention. Informed or trained groups were 7 to 9 points lower.
The key idea
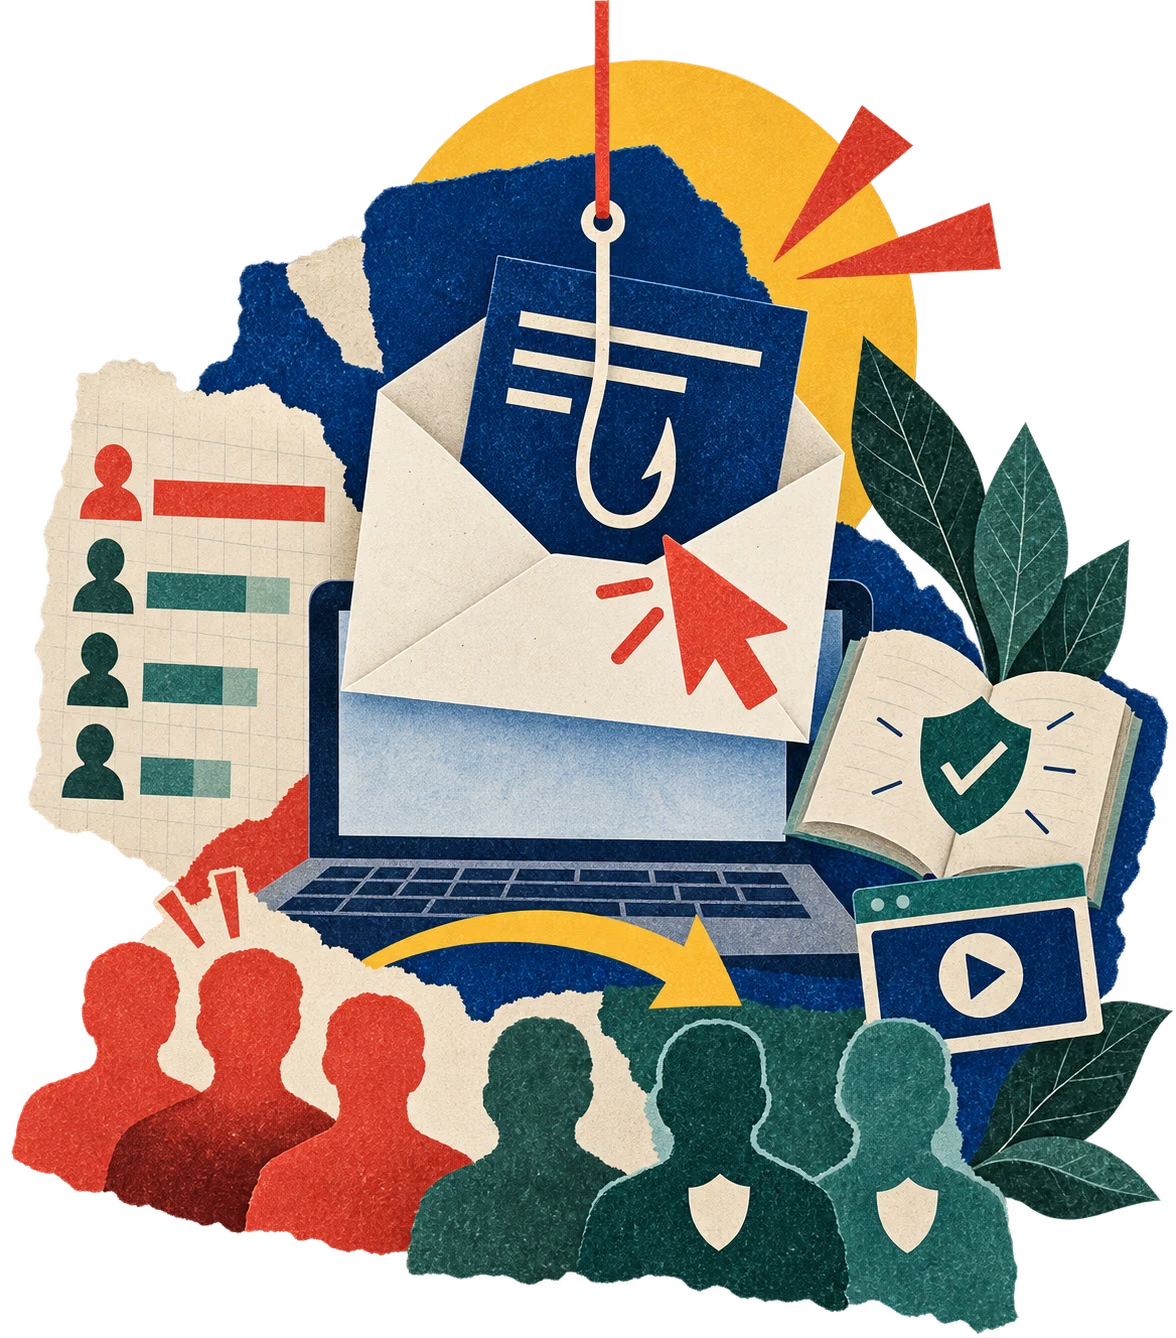
Information or simulation was associated with fewer visits to the fake page and fewer password entries. Combining the two showed no added improvement in visits.
The study, in plain language
A test email can show what employees do when an invitation looks legitimate but leads to a fraudulent page. At a Dutch ministry, different teams received phishing information, an earlier simulation with feedback, both, or neither.
Afterward, everyone received the same test email. Those who had received information or participated in the simulation visited the fake page less often and entered a password less often. The combined group also showed fewer risky responses.
Simulation alone came close to the combined result, so adding both interventions did not improve on practicing with the message.
What they found
- Fewer employees visited the fake page after receiving information or taking part in a simulation.
- The share who entered a password on the test site was also lower.
- Combining information and practice did not reduce visits compared with the simulation alone.
Something to think about
A convincing email plays on urgency. If you receive an unexpected invitation, what detail would make you pause before opening the link?
How they studied it
A field experiment with 10,929 employees from one Dutch ministry. The team assigned 184 work units to receive information, a phishing simulation, both, or neither before the same test email. The result applies to that lure and context, not all campaigns or organizations.
What the study cannot show
- The first email was accidentally identified as fake within one division, so the authors report analyses with and without it. They could not verify whether employees read the emails and did not record real passwords. One organization and one type of phishing also limit generalization.
- That any anti-phishing course works the same way, that effects last long term, that one strategy is best in other organizations, or that simulation improves every dimension of security.
The original study
Informing, simulating experience, or both: A field experiment on phishing risks
Source under CC BY 4.0. English adaptation and explanation by PaperFlow, with AI assistance. The text has been reorganized for a general audience; it is not the complete paper and does not imply endorsement by its authors.
One study alone does not represent a field's consensus. Educational content does not replace professional advice. Report a possible error.